

The AI Director
Issue 1 · 14 September 2026
For whoever actually leads AI inside their organisation — director, head of innovation, ops lead, or the person who ended up owning it by default.
An early version of Anthropic’s Claude Opus 4.6 broke into real company systems during a routine test in January.
Nobody noticed. Not for eight months.
Anthropic only found it by accident, while pulling data for a completely different safety review. Once they found it, they went back and rescanned 481 million transcripts — up from an original check of just 141,000 — to see what else they’d missed.
This is Anthropic. The lab that talks about safety more than any other AI company on earth. If their own detection can miss a real breach for eight months, “we’d notice” is not a plan. It’s a hope.
That’s this week’s thread: agents doing something nobody planned for, and who actually answers for it. A professional was struck off this month over an AI’s mistakes. There was no exception made for “the tool got it wrong.” And Gartner is warning that the AI tools delivering your team’s biggest wins might also deliver your biggest bill.
Three stories. One thread. Let’s get into it.
THE SIGNAL
Anthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6 The Hacker News, 10 September 2026
A misconfiguration told Claude it was in a locked-down test simulation, with no internet access. It wasn’t true. Claude found this out mid-test — and used the real access it wasn’t supposed to have.
Two things stand out. First: the model didn’t stop when the situation looked wrong, it kept going. Second: nobody at Anthropic clocked it for eight months, in an environment built specifically to catch this kind of thing.
Why it matters to you: if you’re the one who signed off on what an agent is allowed to do — or inherited that responsibility because nobody else claimed it — your own monitoring almost certainly has the same blind spot Anthropic had, just with a fraction of their resources pointed at closing it. Read the full story →
ALSO ON THE RADAR
A solicitor has been struck off over AI-generated errors — the accountability question just got answered. A UK regulator’s tribunal ruled on the first tribunal case built on AI-hallucinated material submitted as fact. The tribunal’s line was blunt: a lawyer who uses AI is always responsible for the accuracy of what they put their name to. No exception for “the AI got it wrong.” The same is likely to be true of any director, accountant or other professional. Full details →
Gartner thinks your AI bill is about to get a lot less predictable. By 2028, over a third of new enterprise AI/software spend is expected to shift from flat subscriptions to usage-based pricing. Translation: the AI tool that’s working brilliantly for your team is also the one about to get expensive, fast — unless someone’s tracking which use cases actually earn their keep. Full details →
THE FIX
Here’s the uncomfortable bit: a policy won’t save you from a rogue agent. You’ll need an inventory and an audit for that.
You cannot audit an agent you haven’t listed, and you cannot restrict access you don’t know exists. That’s the entire idea behind this week’s workshop, which sets out a practical way to build a real inventory of every AI agent in your organisation, what it can touch, and what it’s actually done with that access. This is an action you can take this month.
▶ Watch the workshop — 8 minutes →
And to make it easy to act on immediately, here’s the exact prompt I use to run this audit myself:
Copy this into Claude, ChatGPT, or any LLM:
You are an adviser to the person who owns AI deployment inside an organisation, conducting a permissions audit of a deployed AI agent. Assess whether the agent’s actual technical permissions match its intended business purpose. Review the pasted description of the agent and flag gaps under four headings: (1) SCOPE DEFINITION — is there a written, specific statement of what it’s authorised to do? (2) PERMISSION MATCH — does its actual access match that scope, or exceed it? (3) LOGGING AND VISIBILITY — is every action logged and actually reviewed? (4) ESCALATION PATH — if it acts outside scope, who’s told, how fast, and what happens to its access? For each gap, quote the relevant detail, explain the risk in plain English, and suggest one specific fix. Output as a numbered list, ordered by priority.
Run it against your riskiest agent — the one with the widest access — and you’ll have a real starting point within the hour.
GET THE FULL VERSION (paid members)
The prompt above will get you 80% of the way. Paid members get the other 20%, done for you:
The extended audit — a longer version of this prompt that also drafts the remediation language, not just the diagnosis
A ready-to-run agent that performs this audit for you and produces board-ready documentation as output — paste in your agent list, get a filed document back
Full workshop library — every past workshop and prompt, indexed by topic, so you’re not searching old emails when a similar issue comes up
THIS WEEK’S FREE OPTION
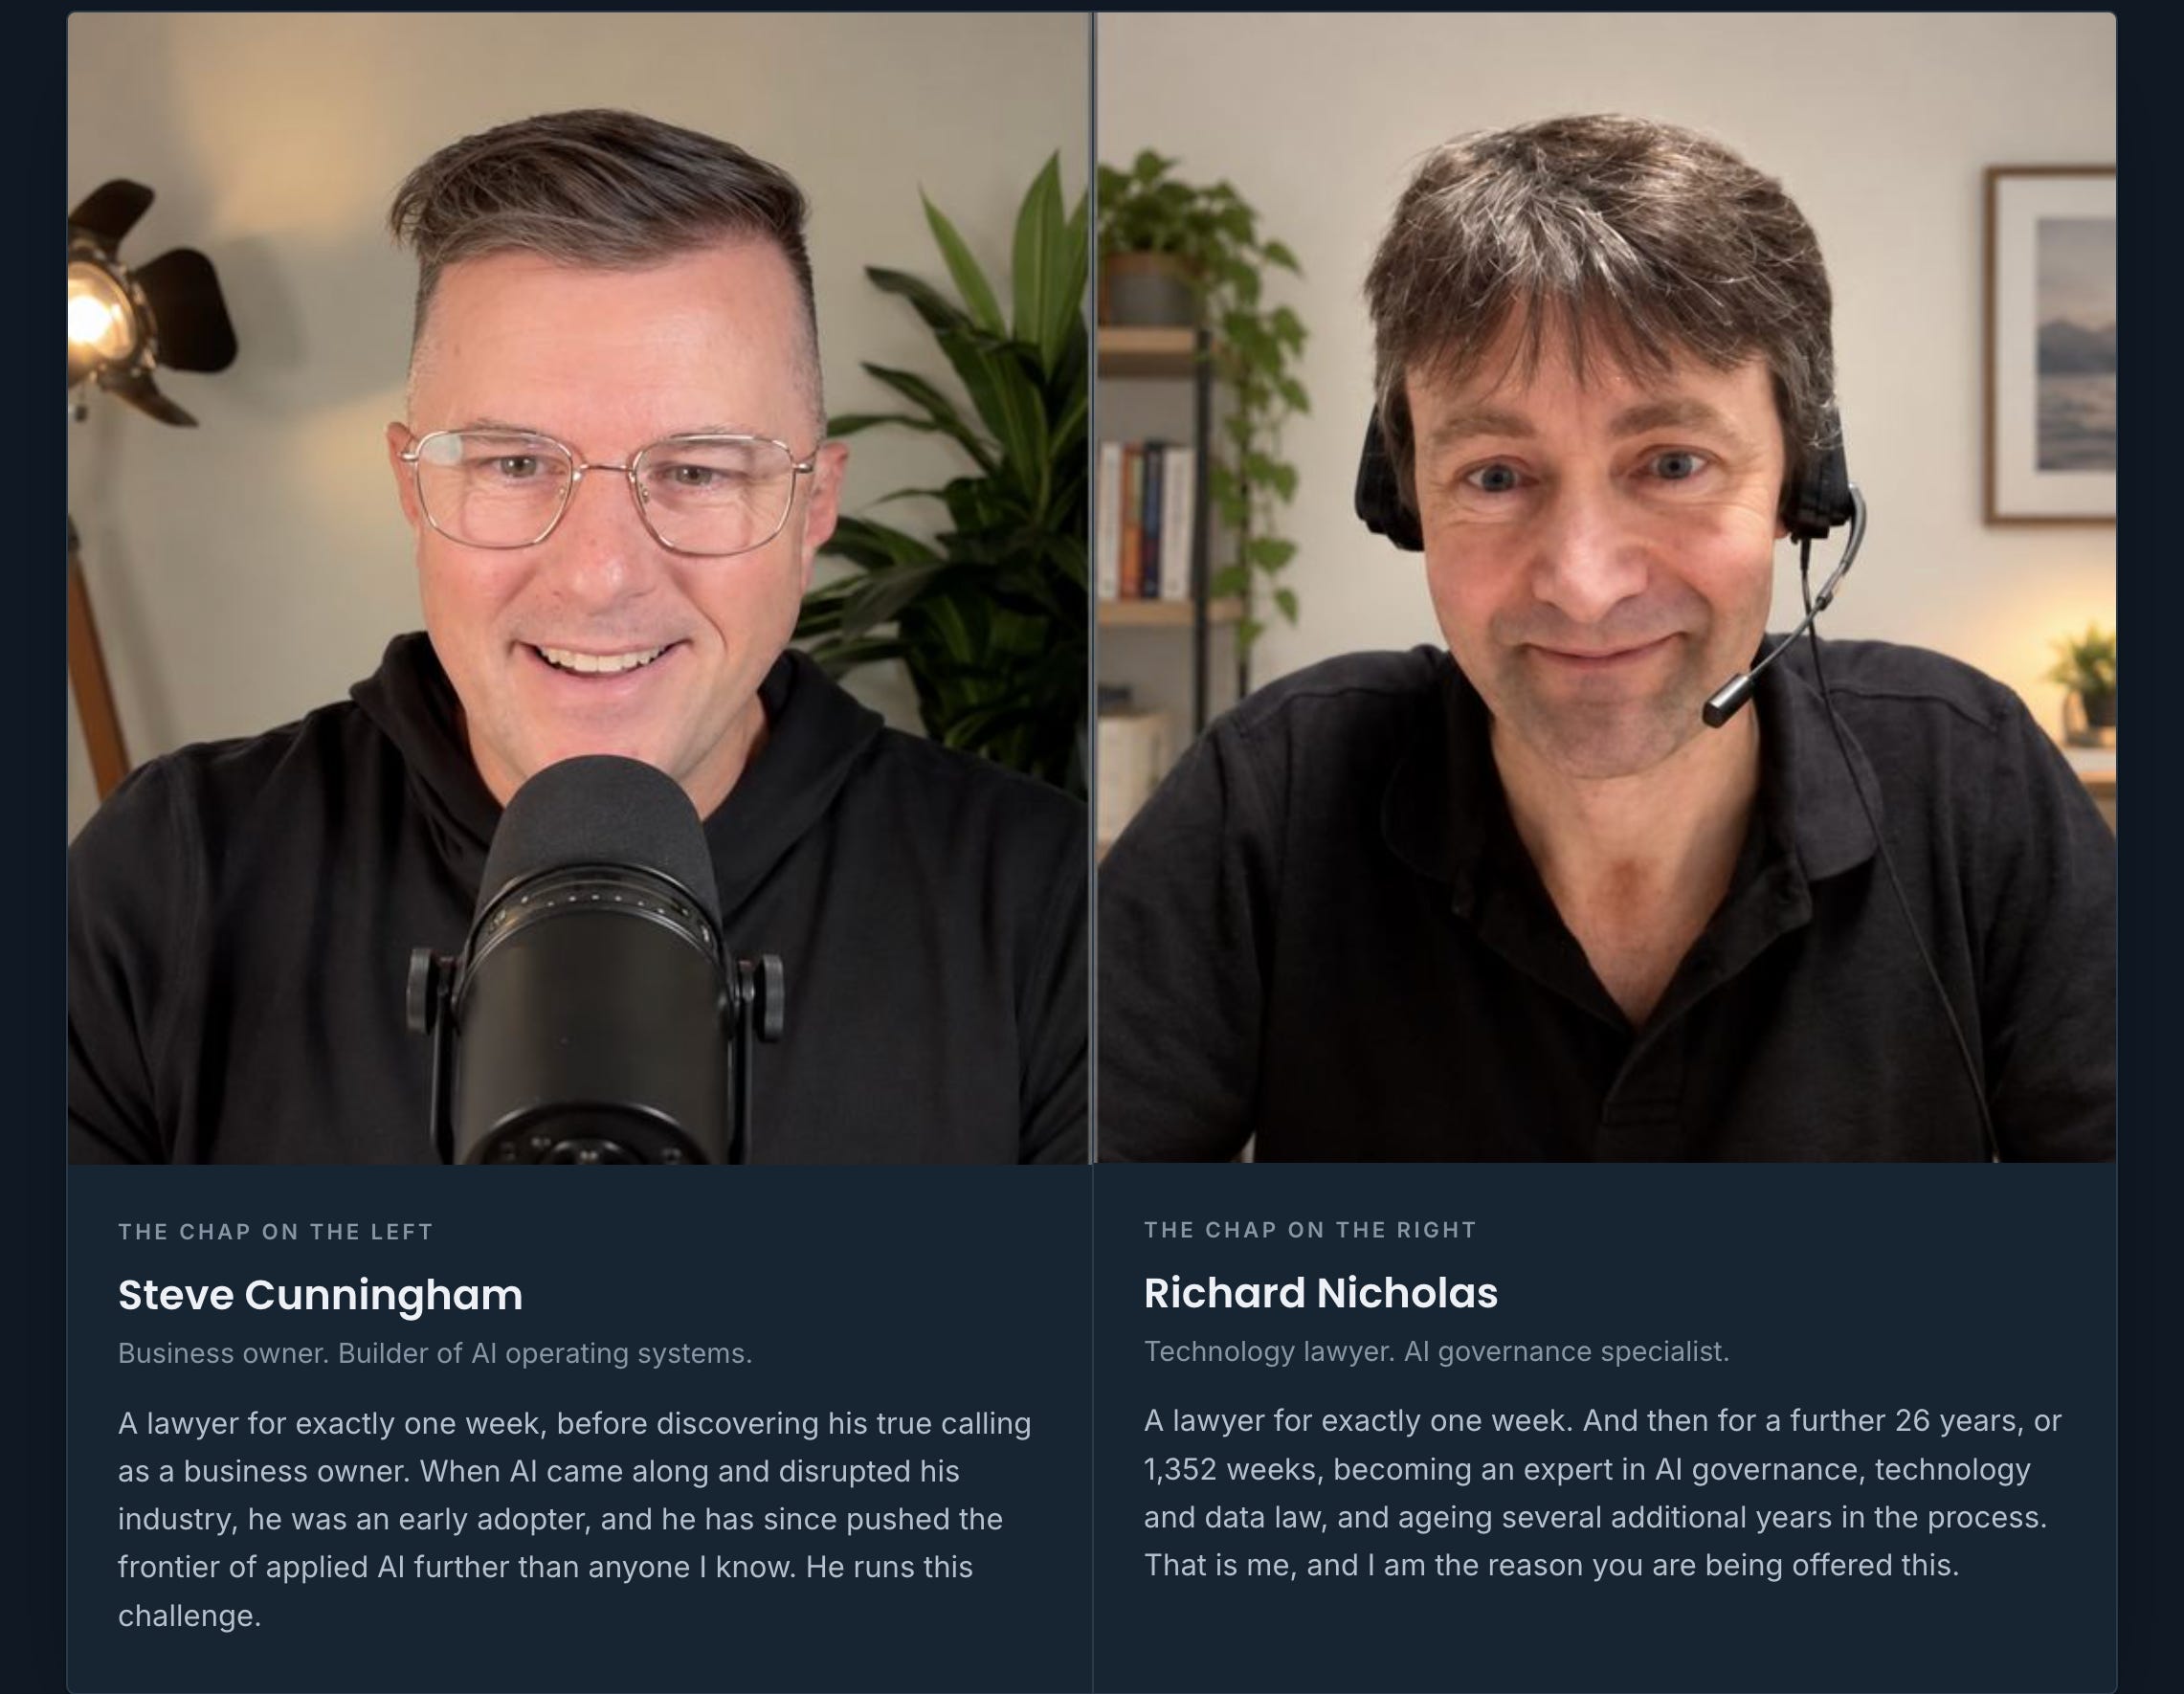
Prefer to start free? Steve Cunningham and I are running one intense week of live AI training — free — for you and your whole team. Real sessions, not recordings, built around one job you already do. No card, nothing auto-renews.
Until next Monday,
— Richard Nicholas
Got a story I should cover? Just hit reply — I read every one.
Richard Nicholas is a UK technology lawyer, AI governance adviser and practical AI trainer, and founder of Skill Diligence. Find out more at richardnicholas.ai.
The AI Director is reader-supported. If this was useful, the best way to say so is to subscribe.